

It’s the start of a new year and alongside the normal best wishes for health and happiness, the new year also presents us with an opportunity to do new things or do old things better.
These opportunities materialise themselves as New Year’s resolutions and represent the desire to change things for the better over the next twelve months. Sadly, normally these resolutions are dead and buried by the end of January and some die in the first week!
But, with a full twelve-month budget cycle ahead, sure there are some resolutions that a company can make, and one’s that will stick, when it comes to risk management and your Oracle E-Business Suite.
I hear you ask, “why bother this year in particular?”. Well, there are a number of good reasons.
Firstly, listed companies in the UK are probably very aware that ‘Section 4 – Audit, risk and internal control’ of the UK Governance Code (UKSOX), delayed to give company’s more time to prepare evidence of the effectiveness of their internal controls, comes into effect fully on the 1st of January 2026. If you are not aware, then follow the link for some interesting reading: https://media.frc.org.uk/documents/UK_Corporate_Governance_Code_2024_a2hmQmY.pdf.
One of the key principles of Section 4 is that “The board should establish and maintain an effective risk management and internal control framework” and that the Board should “….. confirm in the annual report that it has completed [a robust assessment of the company’s emerging and principal risks], including a description of its principal risks, and an explanation of how these are being managed or mitigated.”
So, if you are not 100% sure you have an effective risk management and internal control framework in place, then it needs immediate attention before you have shareholders screaming “why not?” at the end of the year. And note, auditors WILL, in 2026, be looking for that compliance.
Secondly, the spectre of sustaining support for those using Oracle GRC is not going away. If you are still relying on Oracle GRC for your management of risk, then that itself is taking a risk. And if you are central or local government, military or defence contractor or just a large, listed company, that is a massive risk. And if anything goes wrong, you can bet your bottom dollar, people will ask why things weren’t changed. Especially since we are fast coming up on the first anniversary of that ‘bare minimum’ support level.
Finally, those companies that are not listed or not using Oracle GRC, do you not owe it to your shareholders, your employees, your suppliers and, yes, your customers, to take a robust approach to risk management. By have the right processes and procedures in place guards against fraud, overreach, unintended error, unauthorised approvals and the like, you protect the future of your company for your shareholders and all those who rely on it for their living and the continued success of their own businesses.
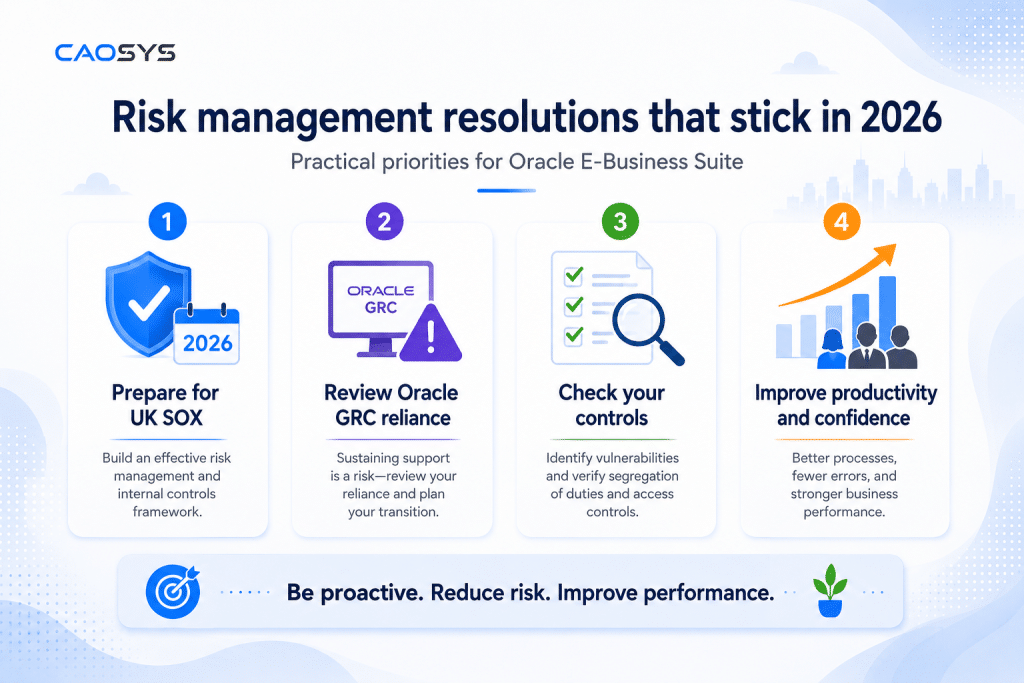
If you think you have it all covered, then why not make a New Year’s resolution to get it checked so, if there are any vulnerabilities you can get them addressed. If nothing more than peace of mind when it comes to those annual reports (being proactive is a wonderful thing).
And if you have any doubts at all, then it is even more important to make that resolution to get it all checked out.
By way of a final thought, it has been proved that proper processes and procedures can deliver a marked increase in productivity as people understand what they need to do and the boundaries under which they operate. Productivity increase means better revenue performance which in turn gives you a successful company and happy shareholders.
If you are going to make that New Year’s resolution and get a review of your strategy when it comes to risk management and internal control frameworks, then we at CAOSYS would recommend a number of key partners you should be talking to:
DSP (https://www.dsp.co.uk/)
Namos Solutions (https://namossolutions.com/)
ERP Risk Advisors (https://www.erpra.net/)
6e Technologies (https://6etech.com/)
CAOSYS provides a comprehensive suite of governance, risk and audit management solutions designed to support SOX and UK SOX compliance across Oracle platforms. Its fully integrated suite of solutions operate directly within Oracle E-Business Suite, enabling organisations to implement and evidence key IT General Controls, including segregation of duties, sensitive access management, periodic user access reviews, and audit trail management controls. These capabilities are complemented by our cloud-based solutions and purpose-built offerings for Oracle Cloud ERP (Fusion Applications), allowing organisations to apply consistent, repeatable and auditable controls across both on-premise and cloud environments.
For further information or if you have any questions or comments, then please mail me at steve.davis@caosys.com.